
 OMM Redaksiyası

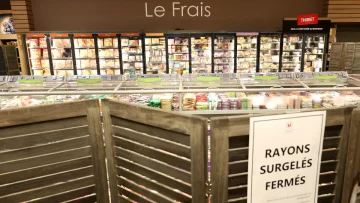
Temperatures in refrigerators and freezers at hundreds of supermarkets in France were raised to as high as 50 degrees overnight. The Paris prosecutor’s office described the incident as a large-scale attack. The attack caused fires and spoiled food.
The owner of French supermarket chain “Intermarché” said about 150 stores were targeted. The refrigerators were heated for six hours, and all food in the stores was discarded to prevent health risks. Another chain, “Carrefour,” said 80 of its supermarkets were affected. The chief executive of retailer “Coopérative U” described the attack as unprecedented.
How did hackers target the cooling systems?
French media reported that hackers interfered with control units for cooling systems made by Danish company “Danfoss,” activating continuous defrost mode. “Danfoss” said it was aware of incidents affecting a limited number of its systems in France. The company said the targeted units were running outdated software.
Security vulnerabilities in this equipment had been identified before. In August, researchers at cybersecurity company “Claroty” found a backdoor in “Danfoss” control units that could give an attacker administrator privileges. They also found that thousands of such units were accessible online. “Danfoss” subsequently released a software patch.
French authorities are investigating the incident. A person at the prime minister’s office said France was coordinating with European partners because other countries could also be affected.
What risks do household devices face?
Internet-connected cameras, doorbells, thermostats and refrigerators can potentially become targets for hackers. At a hacking conference in Las Vegas in 2015, researchers demonstrated that it was possible to compromise a “Samsung” smart refrigerator. The attack could be used to intercept some of the internet traffic passing through the device.
Electrical appliances that connect to the internet or a home network, usually through Wi-Fi, are considered smart devices. These include speakers, fitness trackers and security cameras, as well as refrigerators, thermostats, kettles and washing machines.
Routers used to connect to the internet are also a major target for attacks. According to cloud security platform “Zscaler’s” “ThreatLabz” report from mid-2025, more than 75 percent of attacks on observed connected devices targeted routers.
Cybercriminals mainly seek to collect information or take control of devices. Poorly secured devices and accounts can provide access to personal information, audio and video from toys and baby monitors, as well as home networks. Security officials have warned that live footage from smart cameras and baby monitors sold with easily guessed default passwords could be viewed remotely.
Hackers can also use compromised devices to attack other targets. “Nokia’s” 2023 “Threat Intelligence Report” said the number of poorly secured internet-connected devices used in botnet attacks had risen in a year from about 200,000 to one million. The report listed unsecured smart refrigerators among those devices.
To protect household devices, cybersecurity agencies recommend changing default passwords, choosing a memorable password made up of three random words, and enabling automatic software updates where possible. Manufacturer updates can be installed through the device’s app.
It is also useful to disable remote-access features that are not being used. For example, if the remote viewing function on a camera is not needed, its internet access can be turned off.