
 Afət Ziyadqızı

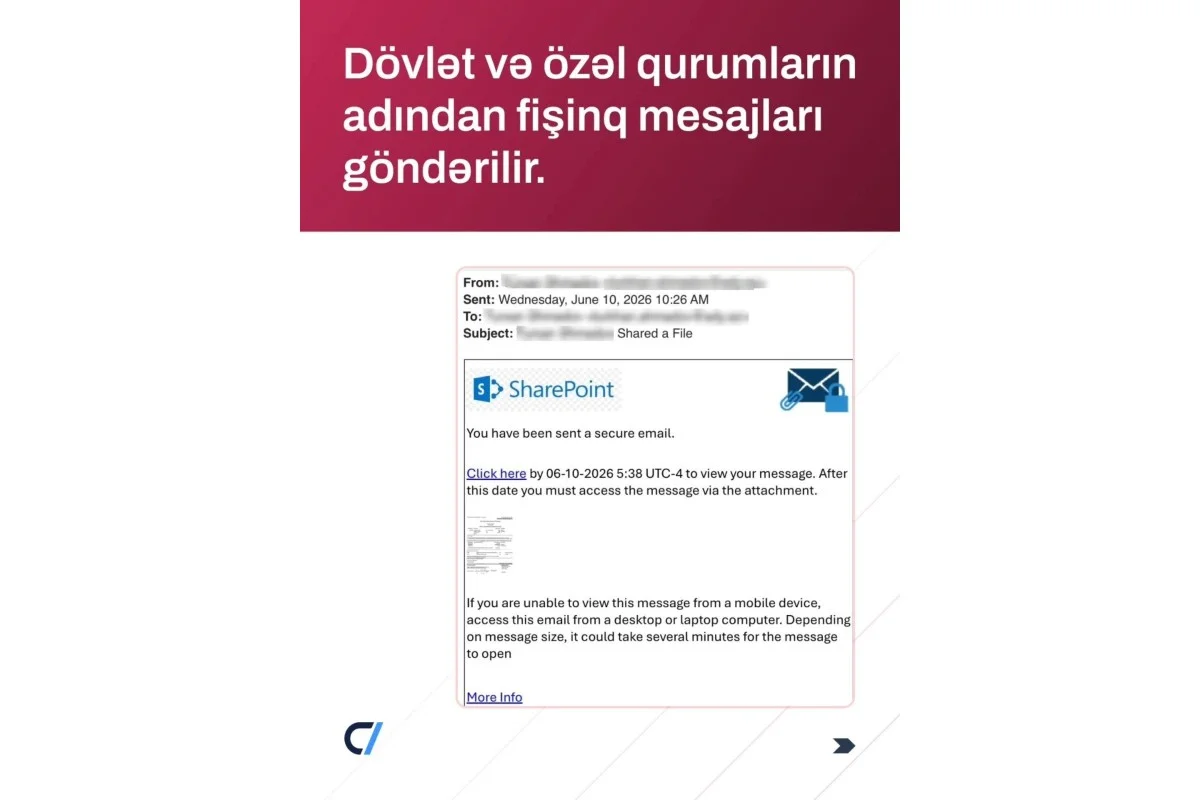
Coordinated attempts to gain unauthorized access to user accounts within several organizations and institutions operating in Azerbaijan have been recorded, according to the State Service of Special Communication and Information Security (SCIS) and the National Cyber Security Center.
This report was disseminated by the Operative Information Center-OMM, citing official data from the National Cyber Security Center.
"Observations indicate that cyber attackers are employing various methods to breach user accounts. In addition to using foreign IP addresses, they are leveraging VPN and proxy infrastructures that provide Azerbaijani IP addresses. This tactic is designed to mask their traffic as legitimate connections originating from within Azerbaijan, thereby bypassing potential geographic security restrictions," the statement noted.
The primary objective of these cyberattacks is to gain unauthorized access to Microsoft 365 environments and other email platforms. By doing so, attackers aim to exfiltrate confidential data, electronic correspondence, and other sensitive information belonging to the targeted institutions.
In response to this threat, the National CERT has issued a series of urgent recommendations for organizations to bolster their account security:
- Conduct thorough audits of login logs, specifically analyzing instances where access is recorded from both foreign and Azerbaijani IP addresses within the same day.
- Investigate multiple failed login attempts targeting various accounts from the same source.
- Identify and isolate any suspicious successful login activities.
- Mandate the activation of multi-factor authentication (MFA) across all user accounts.
The National Cyber Security Center has identified the following indicators of compromise (IOCs) associated with these malicious activities: 146.70.247[.]20, 179.43.158[.]195, 130.94.80[.]141, 94.20.154[.]138, and 35.178.160[.]238.
Cybersecurity incidents of this nature have become increasingly frequent globally as organizations transition to cloud-based infrastructures like Microsoft 365. In Azerbaijan, state agencies and private entities are increasingly prioritizing digital defense mechanisms to protect critical national infrastructure and sensitive data from sophisticated, state-sponsored or criminal cyber threats.